PROVEN
Concurrent mutex — Certificate of Formal Verification (ALL CHECKS PROVEN)
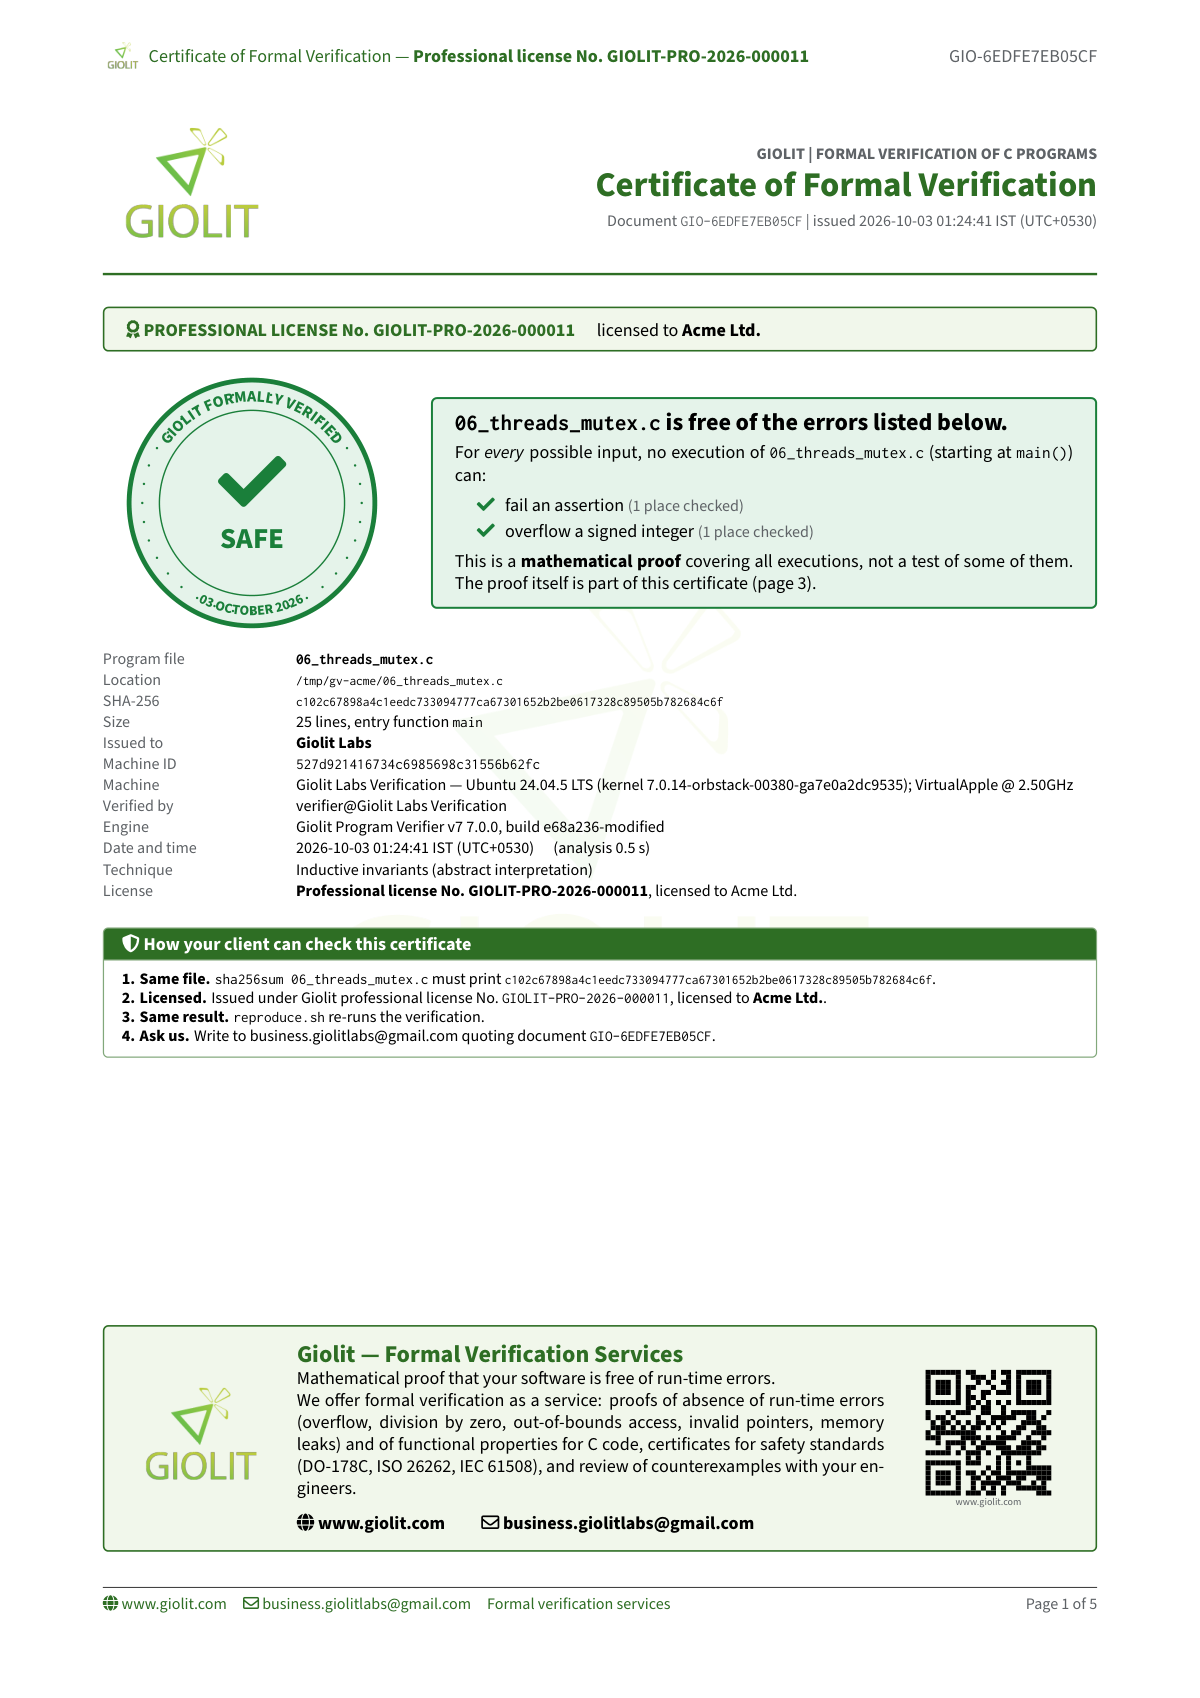
06_threads_mutex.c · entry main · 25 lines · 1 file · 2/2 PROVEN · 0.5s
Giolit Labs advances the science and engineering of high-assurance software systems — the formal specification, proofs, formal verification, formal methods, synthesis, testing, and integration of systems whose correctness, safety, security, and reliability are of critical importance.
Computational artifacts we verify
Formal Verification.Built for High-Assurance Software & Hardware.
Prove C projects free of run-time errors — or prove every SystemVerilog assertion of your RTL for all inputs. Proof, not sampling, with a certificate from every run.
Giolit Program Verifier 7.0
A Complete C projects formal verifier. Until now only single functions could be formally verified — Giolit Verifier proves end-to-end projects spanning multiple files. The C project may include multiple threads or recursions, multiple functions and multiple files. Testing tries a few inputs; a proof covers every input. Correct code comes back proven safe, buggy code comes back with the exact input that breaks it — and every run ends with a certificate carrying the full evidence. Blazing fast: 0.5s thread proof, 16s 35-file project entry, ~10s median.
Proof for every input
Correct code comes back proven safe for all inputs — not just the ones you tested.
Exact failing input when buggy
Buggy code comes back with the exact input and step-by-step trace that breaks it.
Certificate with full evidence
Every run ends with a certificate or report holding the full evidence, ready to share.
0.5s
Mutex proven
16s
35-file project entry proven
~10s
Median per benchmark
Blazing fast and battle-tested: 177 benchmarks — 102 proven safe, 75 real bugs found, zero wrong answers.
Proof, not promises
Real certificates produced by the verifier — open the PDFs and inspect the evidence for yourself.
06_threads_mutex.c · entry main · 25 lines · 1 file · 2/2 PROVEN · 0.5s
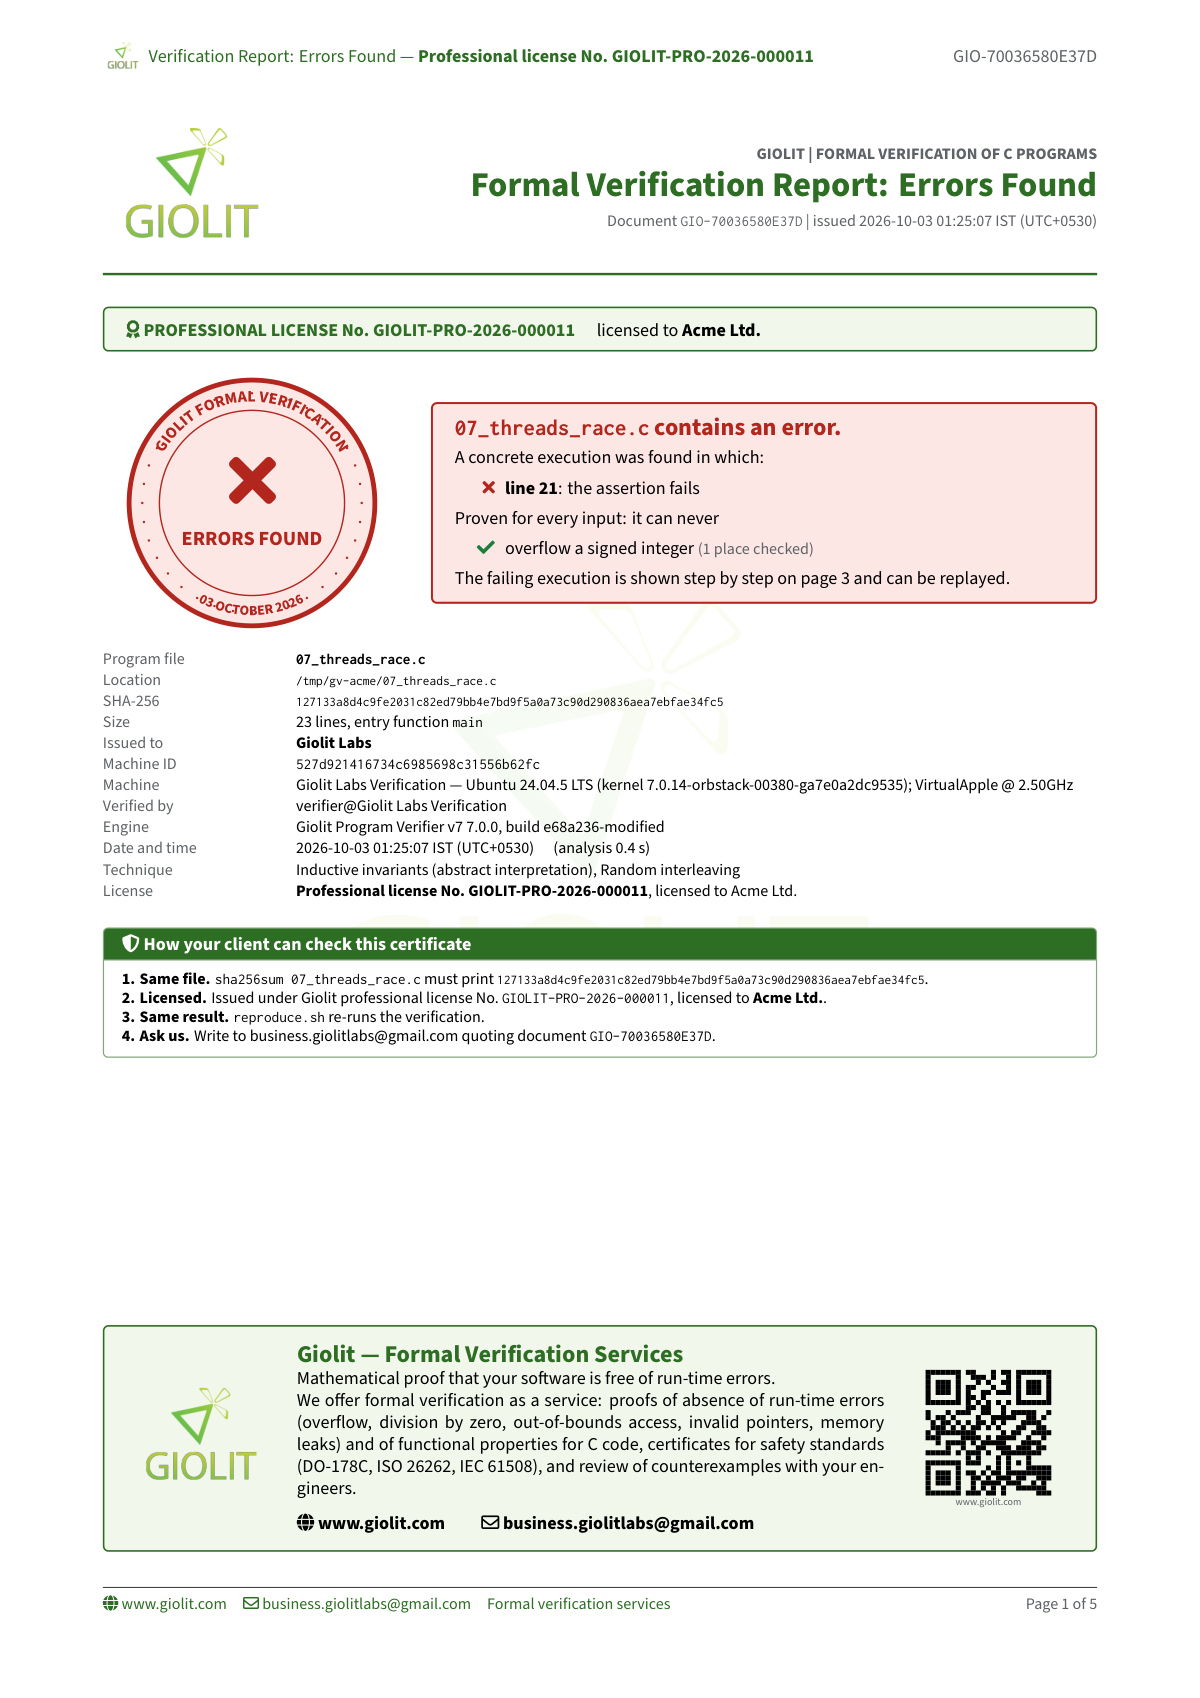
07_threads_race.c · entry main · 23 lines · 1 file · 1 proven / 1 violated · 0.3s
Shows the exact failing interleaving and trace.
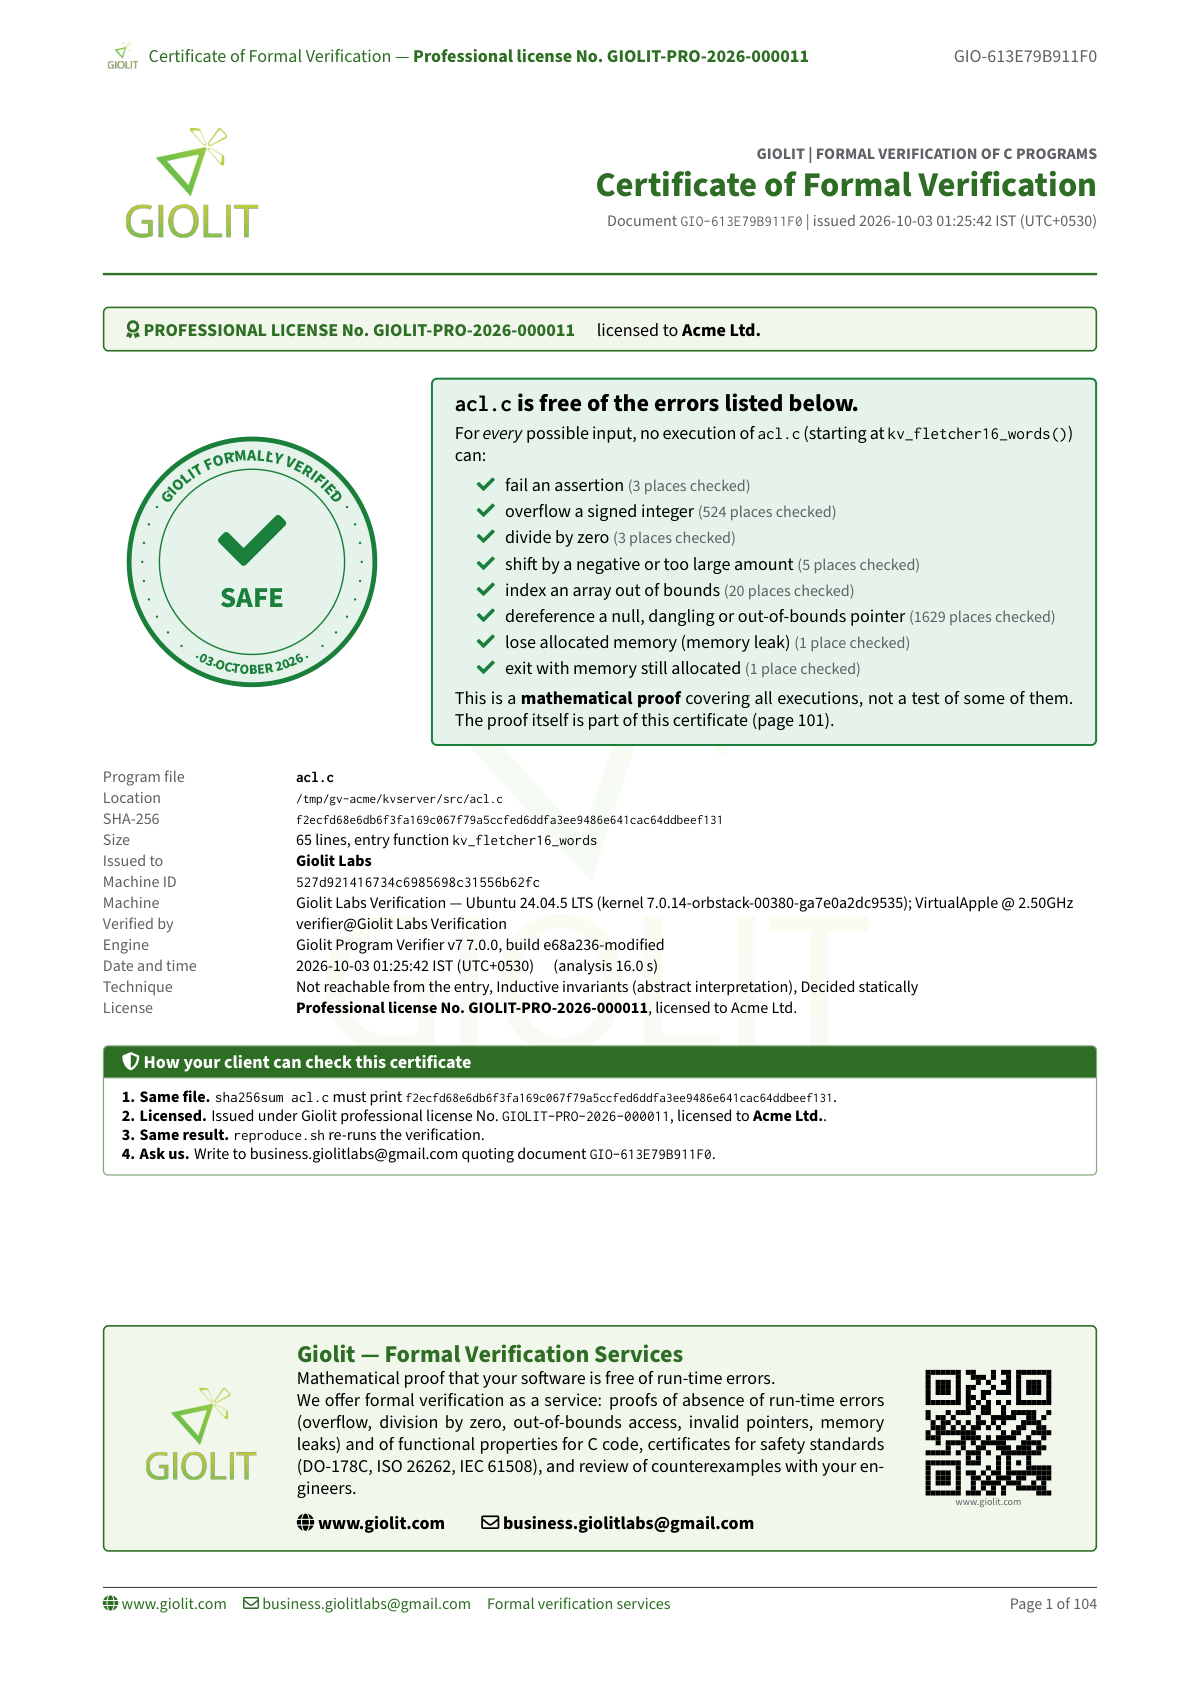
kvserver src/*.c · 35 files / 4870 lines linked end-to-end · entry kv_fletcher16_words · 9 proven / 0 violated · 16s · 104-page PDF
Technical detail: verification covers multiple threads (POSIX threads and C11 atomics), recursion, and multiple functions and files. Every run yields a certificate or report with full evidence (PDF + JSON + SARIF + proof).
Giolit SVA Verifier 1.0
Simulation checks the input sequences somebody wrote — sva-verify --reset=rst design.sv checks all of them. It reads your RTL hardware with its SystemVerilog Assertions (SVA) as written — no test vectors, no engines to pick — and decides every property: PROVED, with a signed certificate your customer can check and the safety margin each proof holds; or FAILED, with the exact clock-by-clock run that breaks it. The expensive bugs are the sequences nobody simulated — corner cases it finds on day one, with covers and liveness decided in the same run. It runs offline on your machines and gates CI with exit codes and JSON.
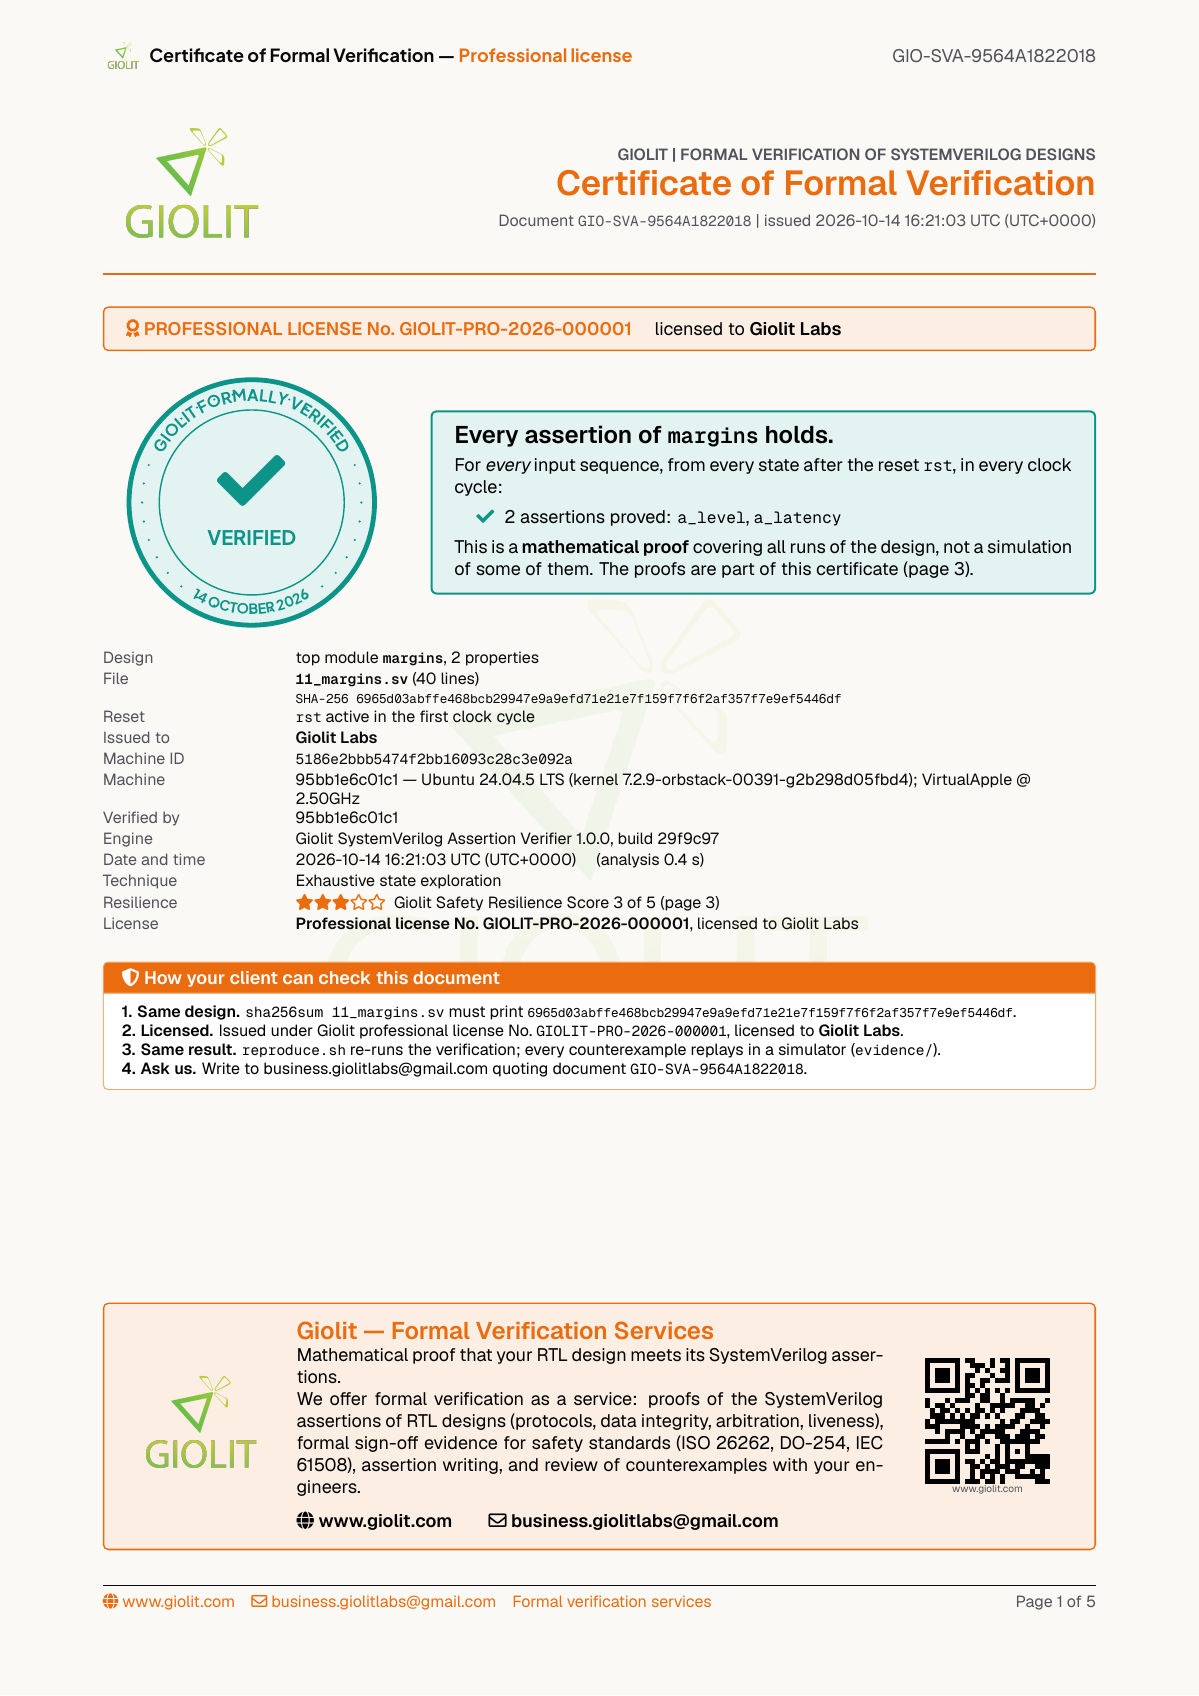
PROVED
Margins proof — stars included
2 PROVED · Score ★★★☆☆ · 5 pages
GIO-SVA-9564A1822018 · signed
Download PDF
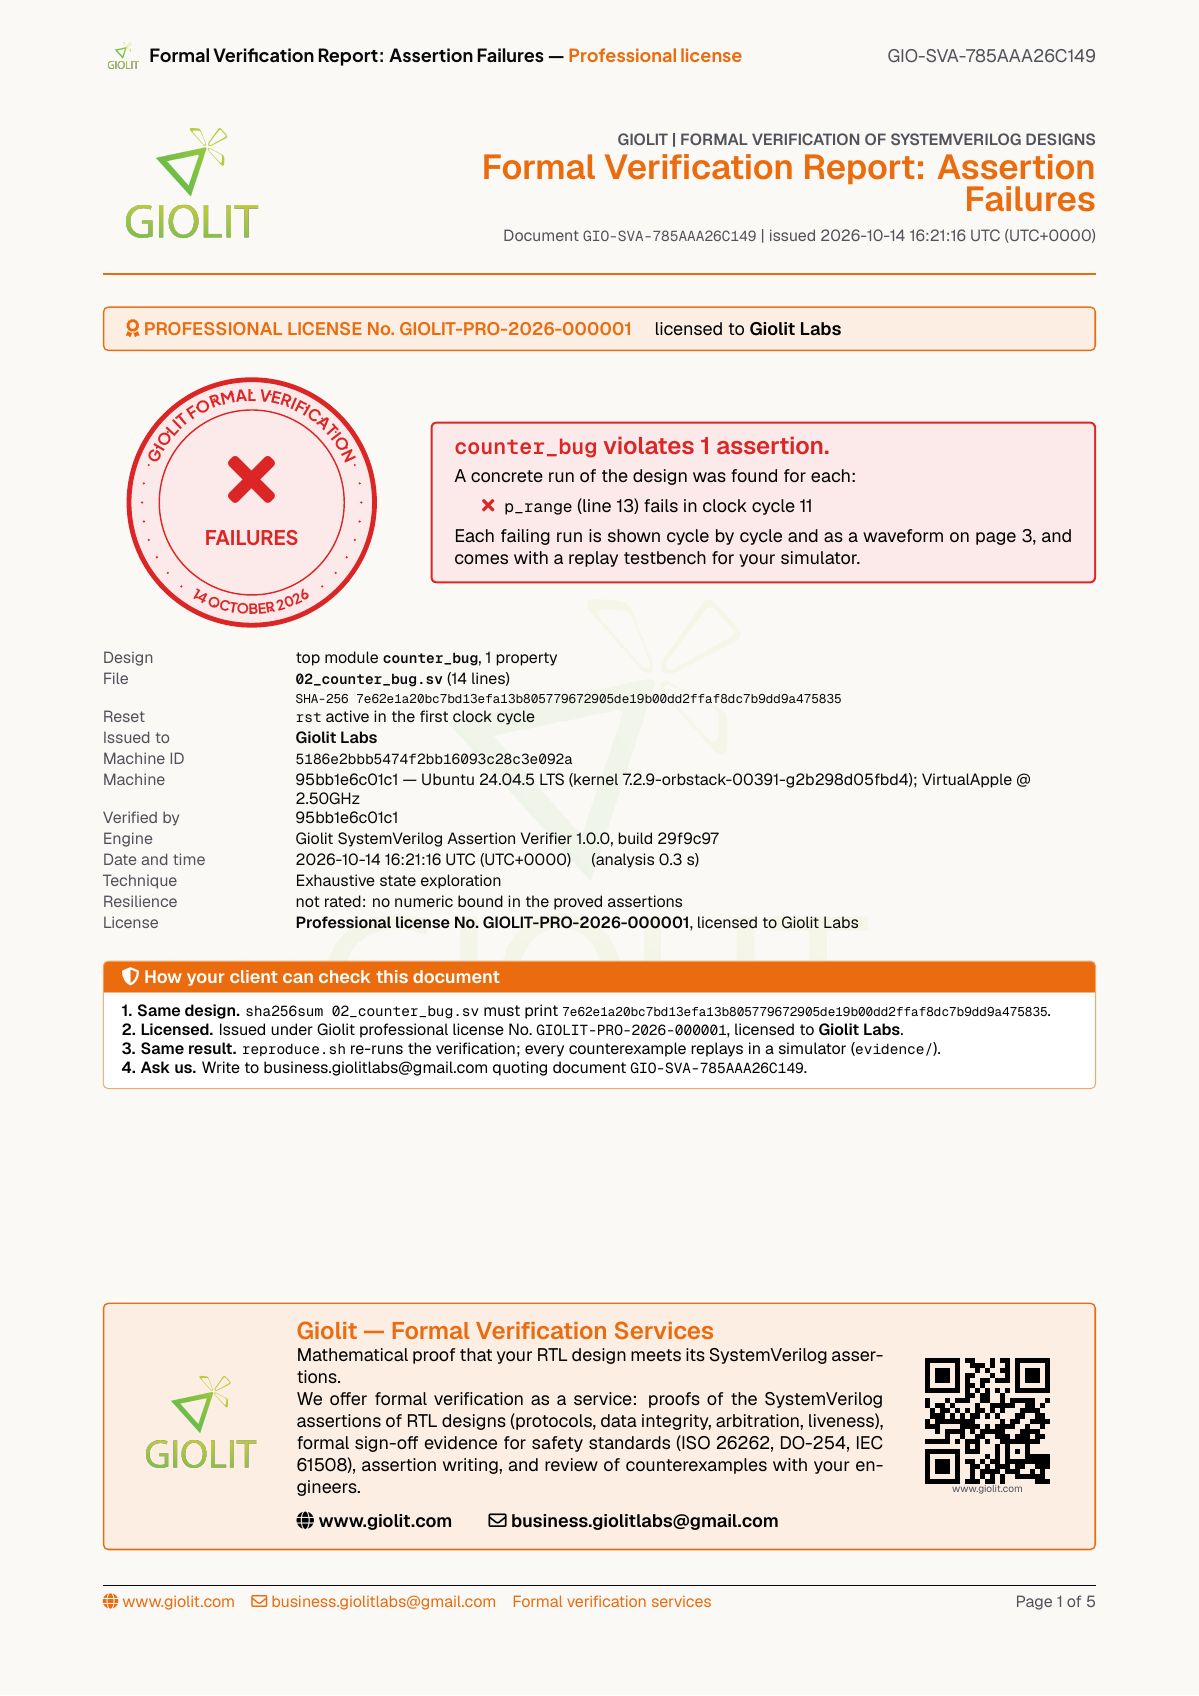
FAILED
Caught bug — the exact cycle
12-cycle trace + VCD + replay · 5 pages
GIO-SVA-785AAA26C149 · signed
Download PDF
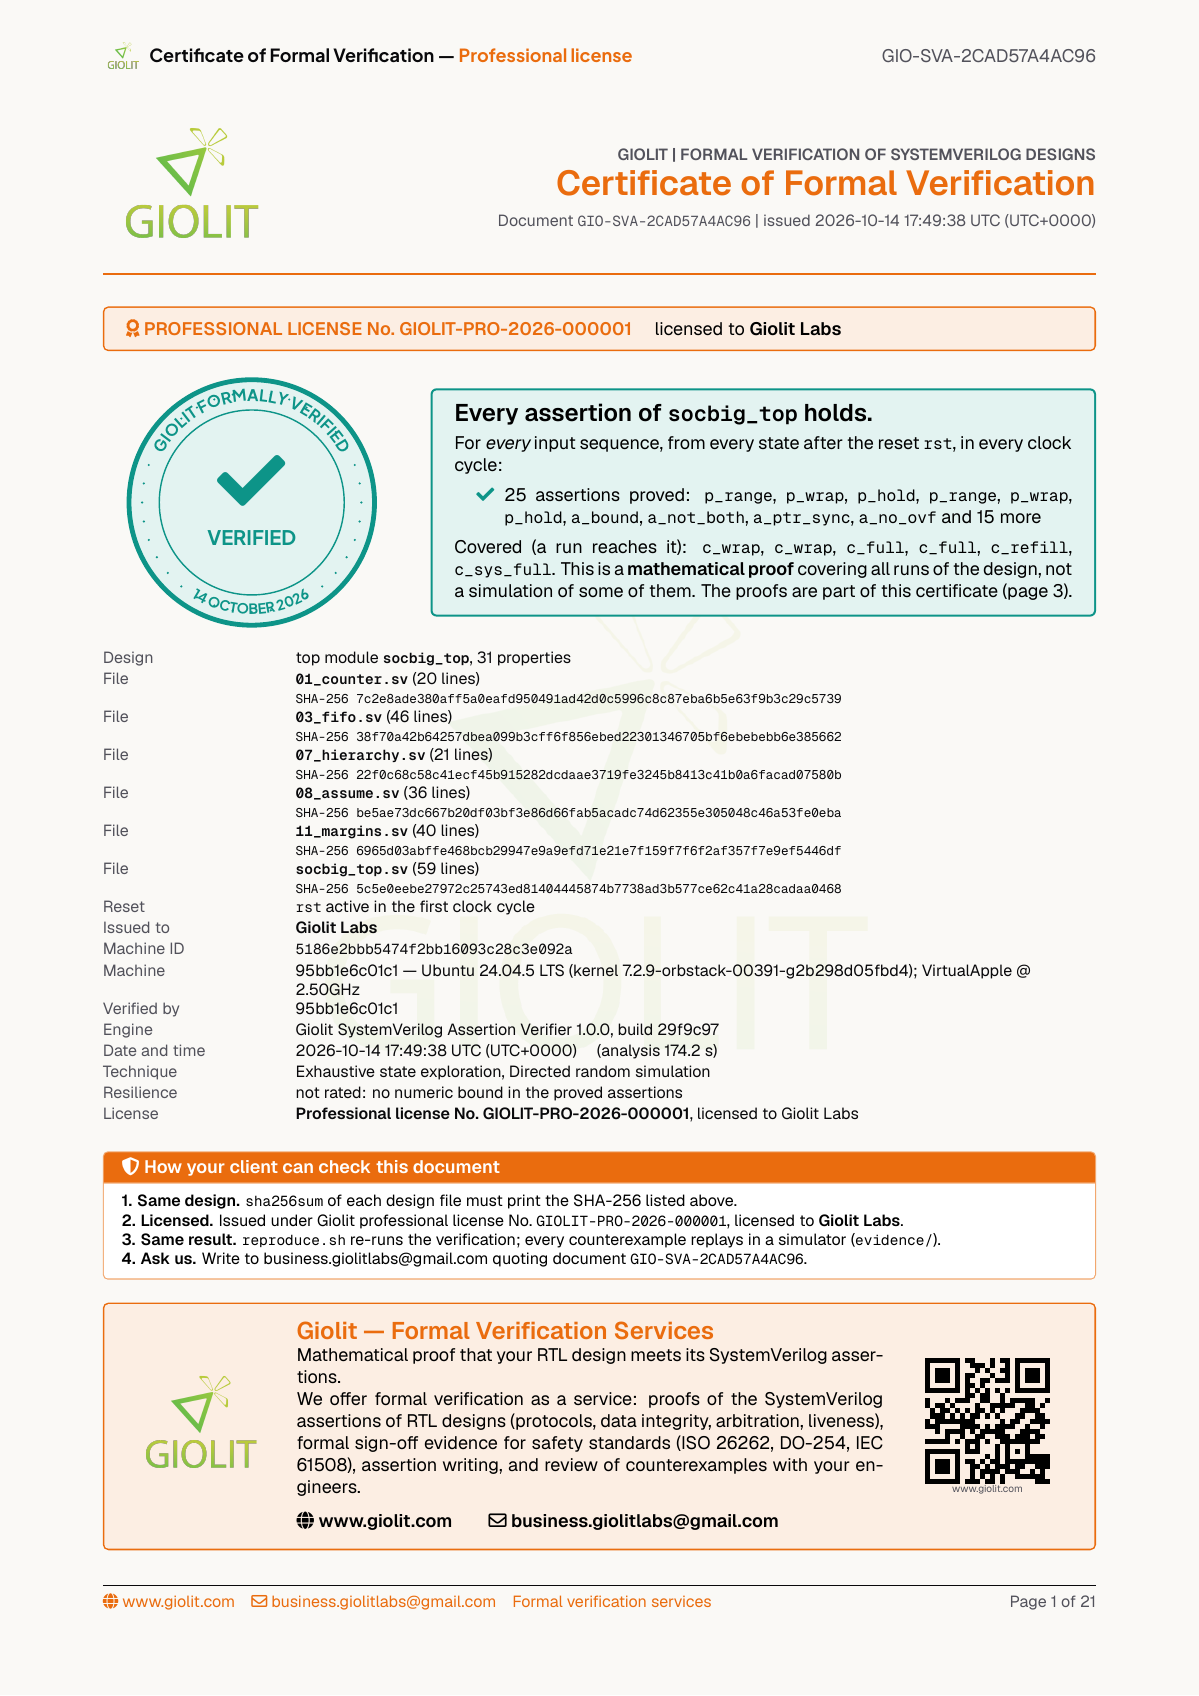
PROVED
SoC proof — 7 files, one certificate
25 PROVED + 6 COVERED · 21 pages
GIO-SVA-2CAD57A4AC96 · signed
Download PDF
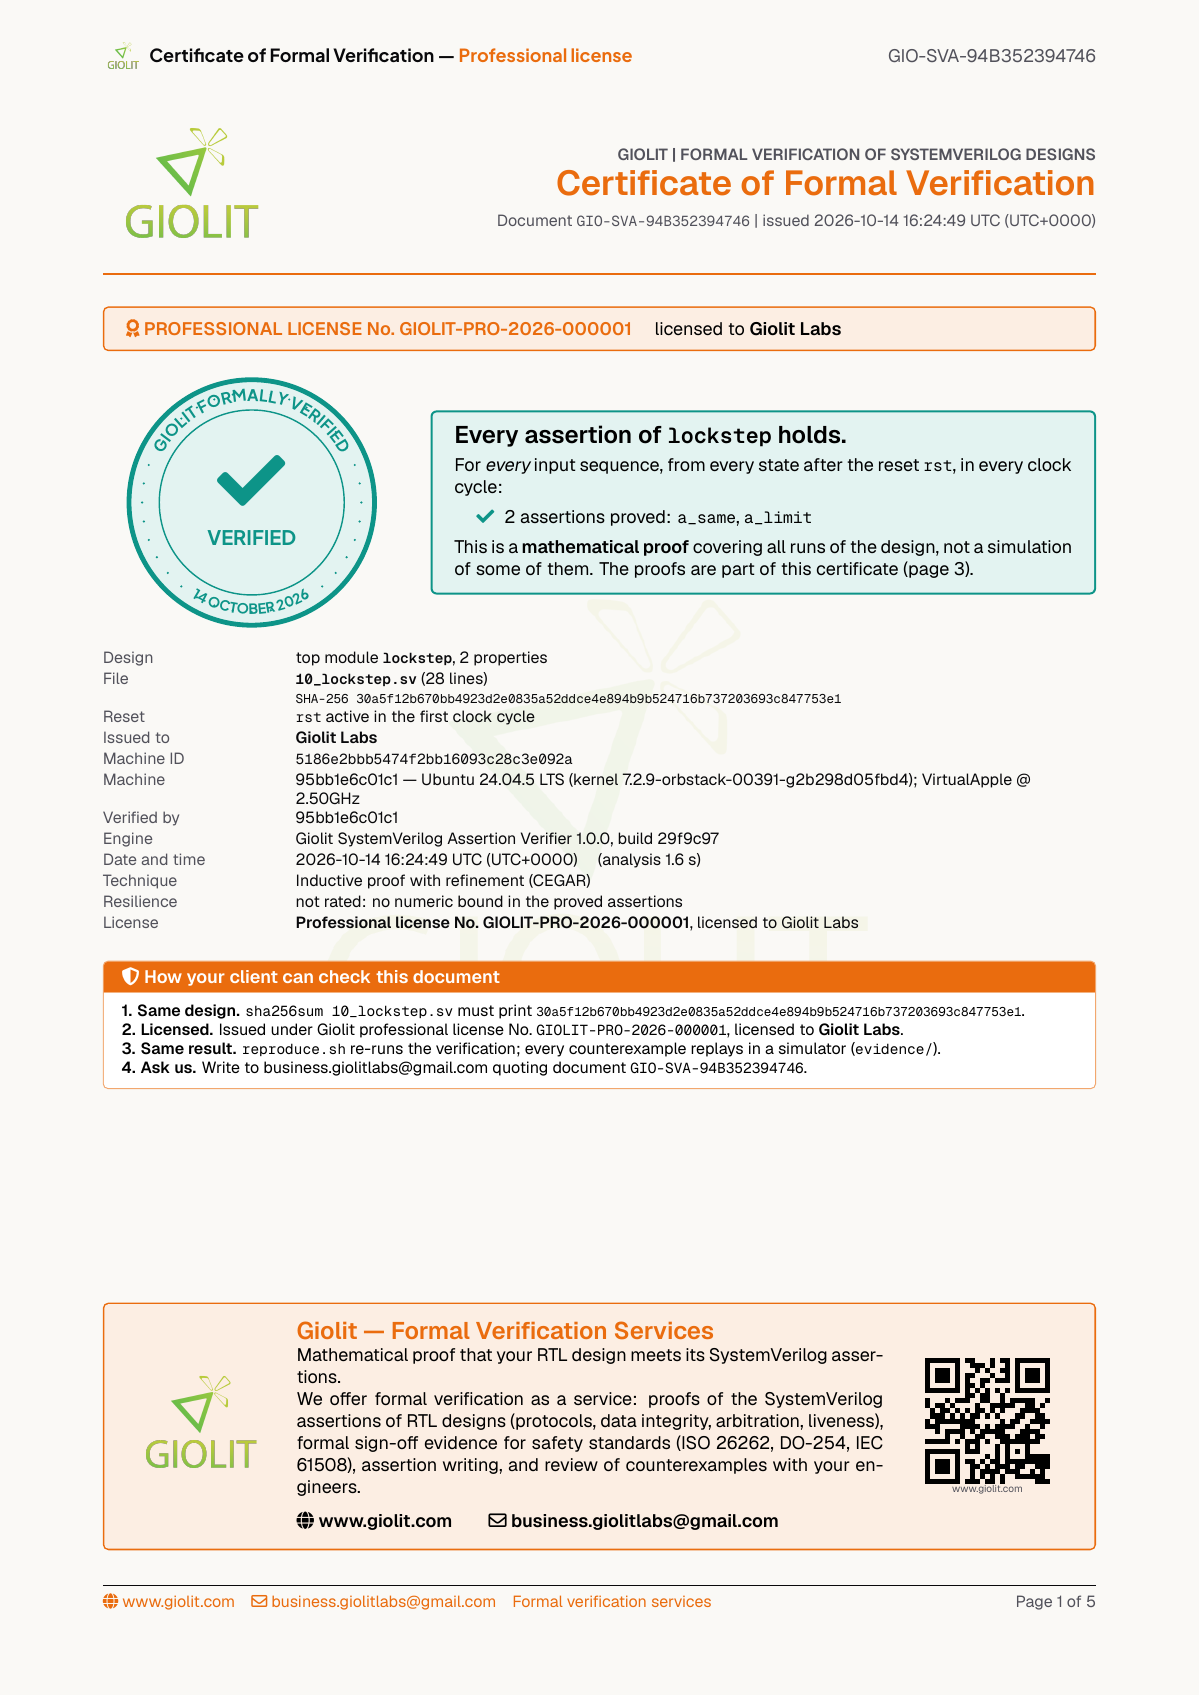
PROVED
Lockstep proof — 12M states, 3 lines
2 PROVED in 1.5 s · 5 pages
GIO-SVA-94B352394746 · signed
Download PDF
$ sva-verify --reset=rst --margins 11_margins.sv
PROVED a_level margin 3 ★★★☆☆
PROVED a_latency margin 3 ★★★★★
Score ★★★☆☆ (3/5) · Report: cert/certificate.pdf
Measured receipt · same 20s budget per design
designs decided, of 231 · 0 wrong on 340 props
Skeptic's note: on 12 bit-level TACAS netlists, abc pdr and EBMC win (7, 6 vs 4) — their home turf. Where SVA language matters, the scoreboard above holds. Every result reruns from the trial package.
Marketplace — Ecosystem of Healthcare Software Components
A marketplace for healthcare software components that enables organizations to discover, integrate, verify, and deploy interoperable software solutions efficiently and reliably — every component ships verification-ready and interoperable, preserving correctness guarantees across integrations.
The marketplace facilitates
Integration-first by design. Every component ships verification-ready and interoperable — so teams can integrate verified modules into larger systems while preserving correctness guarantees.
Assurance Differentiator
Every component is formally specified, verification-ready, and Giolit-signed. Built with IEC 62304 alignment and HL7 / FHIR interoperability support.
IEC 62304
Aligned lifecycle
HL7 / FHIR
Native interoperability
Giolit-Signed
Every module, before deployment
HMS functional coverage — reference
Real-world execution isn't linear. Navigate complex constraints, resource gaps, and safety policies with mathematical proof of goal reachability.
About Us
Our methodologies are founded upon formal methods, automated reasoning, model checking, theorem proving, constraint solving, abstract interpretation, program synthesis, and software assurance techniques. We develop advanced technologies for the automated verification, synthesis, and integration of software ecosystems — and for the seamless integration of verified components into larger systems while preserving correctness guarantees.
Vision
To establish a unified framework for specification, verification, synthesis, testing, and integration that enables the systematic construction of trustworthy software ecosystems with mathematically demonstrable correctness properties.
Core Competencies
Computational Artifacts We Cover
Mission
To enhance the reliability, safety, security, and correctness of software ecosystems through mathematically rigorous verification techniques — and to advance the state of the art in software assurance, enabling the systematic construction of trustworthy computational systems with mathematically demonstrable correctness properties.
Services
Project-delivered verification, testing, synthesis, and engineering — each engagement grounded in formal methods, each result backed by mathematical evidence.
TEST
Comprehensive testing and validation services for complex software-intensive systems.
Capabilities
VERIFY
Rigorous mathematical verification of system properties through automated and semi-automated reasoning techniques.
Verification Targets
Properties Verified
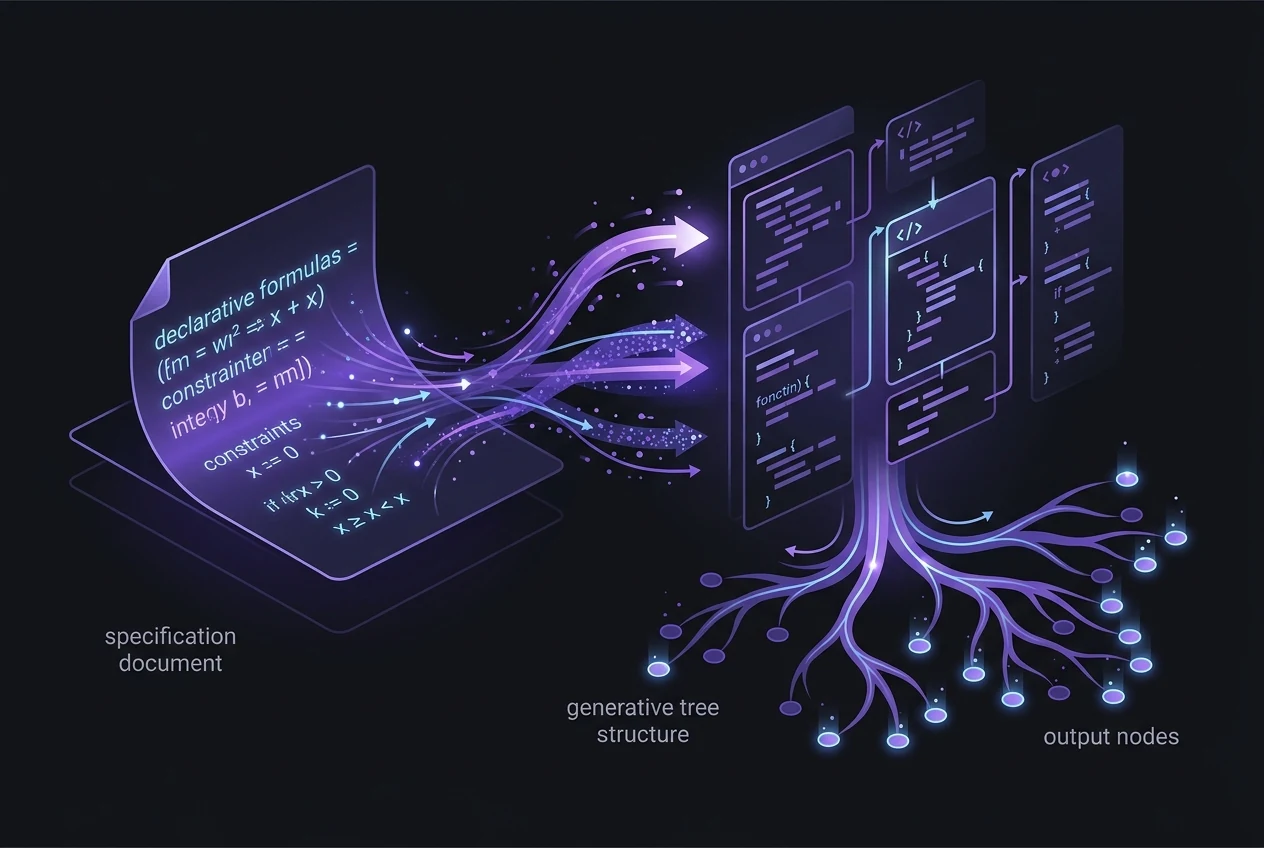
GENERATE
Generation of software artifacts from formal specifications, models, and declarative requirements.
Research Areas
BUILD
Development of software systems in which verification activities are integrated throughout the engineering lifecycle.
Application Domains
Consulting
From a single verification study to an organization-wide assurance program — we advise on process, methodology, and the engineering culture that makes correctness sustainable.
Engagement starts with a focused advisory scope and scales to embedded, long-term partnership on assurance programs — from a single verification study to organization-wide process engineering.
Mathematically rigorous methods to establish correctness properties of software and hardware systems.
Advanced testing infrastructures, automated test generation frameworks, fuzzing technologies, and validation pipelines.
Design, development, integration, and deployment of dependable software systems with emphasis on quality, traceability, and assurance.
Verification-oriented software development processes suitable for safety-critical and mission-critical applications.
Collaboration with academic, industrial, and governmental organizations on advanced verification and assurance technologies.
Tools & Research Platforms
Proprietary tools and platforms built from our research — covering verification, synthesis, testing, and integration. These are the same engines that power our services and underpin every product we ship.
Tools
Constraint Horn Clause solving for verification backends.
End-to-end automated verification of programs.
Verification of control logic and embedded controllers.
Synthesis of programs with correctness guarantees.
Synthesis of verified controllers.
Intelligent fuzzing for vulnerability and edge-case discovery.
Simulation and behavioral analysis of AI models.
Composition of heterogeneous components with preserved correctness.
Research Platforms
Formally verified enterprise orchestration ensuring constraint-aware execution and mathematical goal reachability guarantees.
Automated verification of software systems against formal specifications and correctness requirements.
Analysis and verification of control logic under diverse operational conditions.
Formal analysis of safety, robustness, and behavioral properties of machine learning systems.
Intelligent generation and execution of test suites for software validation.
Synthesis of software components from formal specifications with correctness guarantees.
Integration of heterogeneous software components while preserving behavioral consistency and system-level correctness.
Standards & Assurance
Our methodologies are applicable to systems developed under assurance and certification frameworks — including those governing medical, automotive, aerospace, railway, and secure software development.
Industries we serve
ISO 26262
Automotive functional safety
IEC 61508
Functional safety of E/E/PE systems
IEC 62304
Medical device software lifecycle
DO-178C
Airborne systems software
EN 50128
Railway software
MISRA
Software development guidelines
Secure SD
Secure software development standards
Continuously applicable across
Engage Giolit Labs
Whether you’re deploying a hospital management system, verifying a safety-critical controller, or engineering an assurance program — we apply formal methods, mathematical proofs, and rigorous formal verification techniques from specification to deployment.
Direct
giolitlabs@gmail.comLocation
Giolit Labs, Ramavarmapuram